This guide covers how Azure DevOps for Jira is architected on Atlassian Forge, what data it stores versus simply passes through, and how long each is retained.
This document related to Azure DevOps for Jira.
Azure DevOps for Jira runs entirely on Atlassian Forge. All app data is stored and processed on Atlassian infrastructure.
At a glance
|
Topic |
Answer |
|---|---|
|
Hosting |
Atlassian Forge, on Atlassian infrastructure. |
|
Credentials |
PATs and webhook credentials are stored only in the Forge Secret Store, never returned to the client, and masked in logs. OAuth tokens (Create branch) are held by Atlassian's Forge OAuth provider; the app never sees them. |
|
Commits, branches, pull requests, builds, deployments |
Passed through to Jira. Not stored by the app. |
|
Work items, comments, attachments |
Passed between Jira and Azure DevOps. Not stored by the app; only identifiers and file metadata are kept for deduplication. |
|
Logs |
Atlassian Forge logs, event metadata only, retained 30 days. Site admins can disable developer access. |
|
After uninstall |
Atlassian retains Forge storage for 28 days, then deletes it. |
Architecture
The app has two main features sharing the same infrastructure:
-
Dev Activities in Jira - shows Azure DevOps commits, branches, pull requests, builds and deployments in Jira, and lets users create branches from Jira.
-
Work Items Sync - keeps Azure DevOps work items and Jira issues in sync, optionally including comments and attachments.
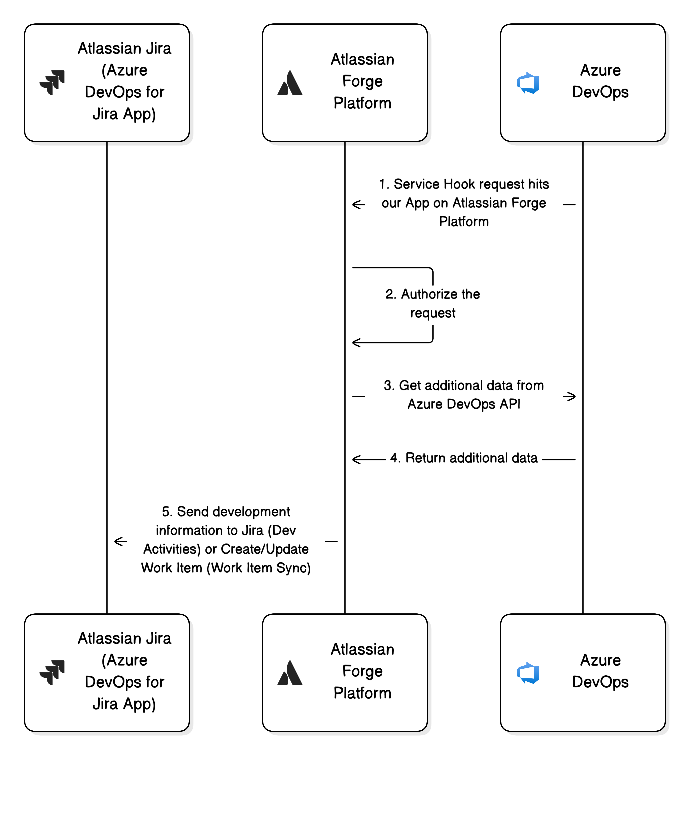
Both receive Azure DevOps events through Forge web triggers, process them via Forge async queues, and call the Azure DevOps and Jira REST APIs.
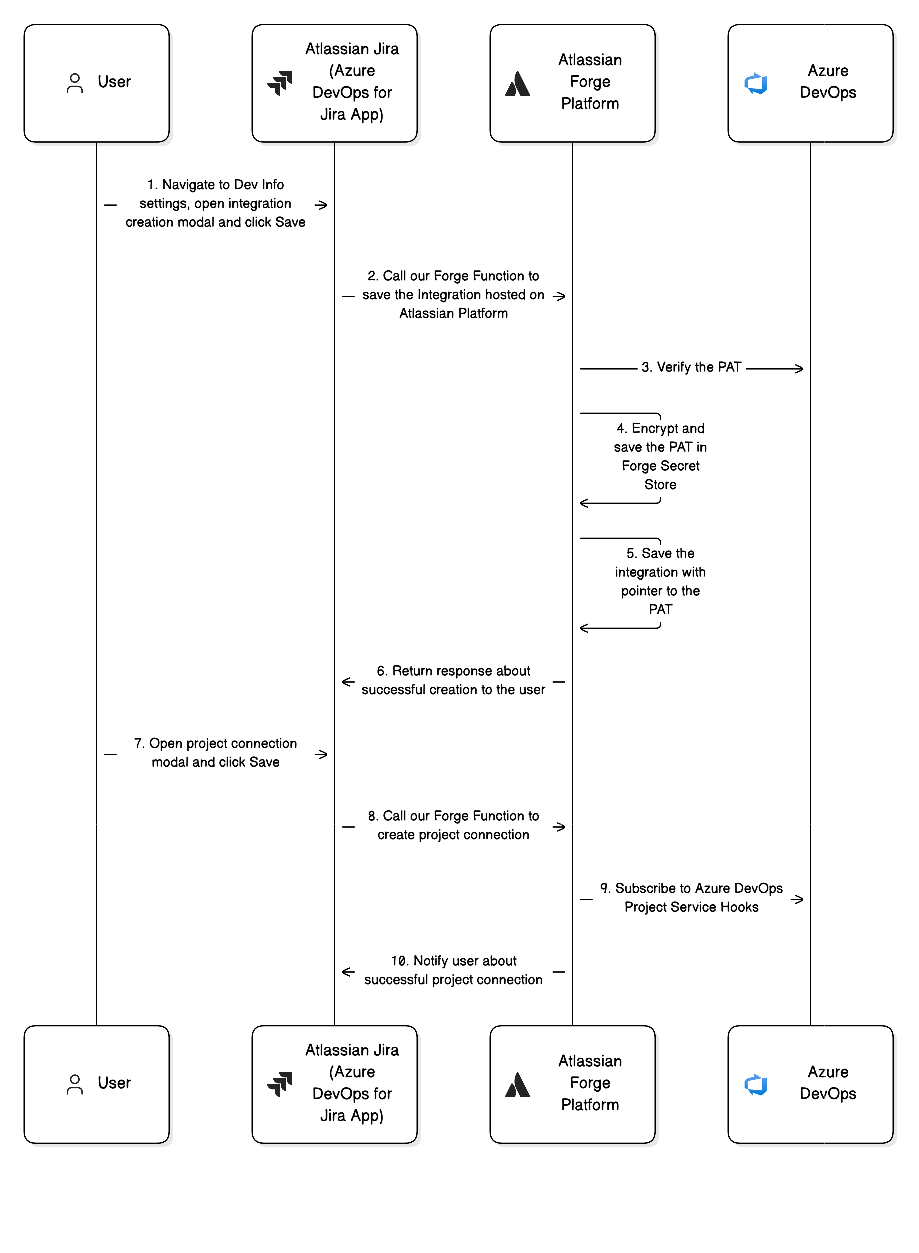
Dev Activities Setup Flow
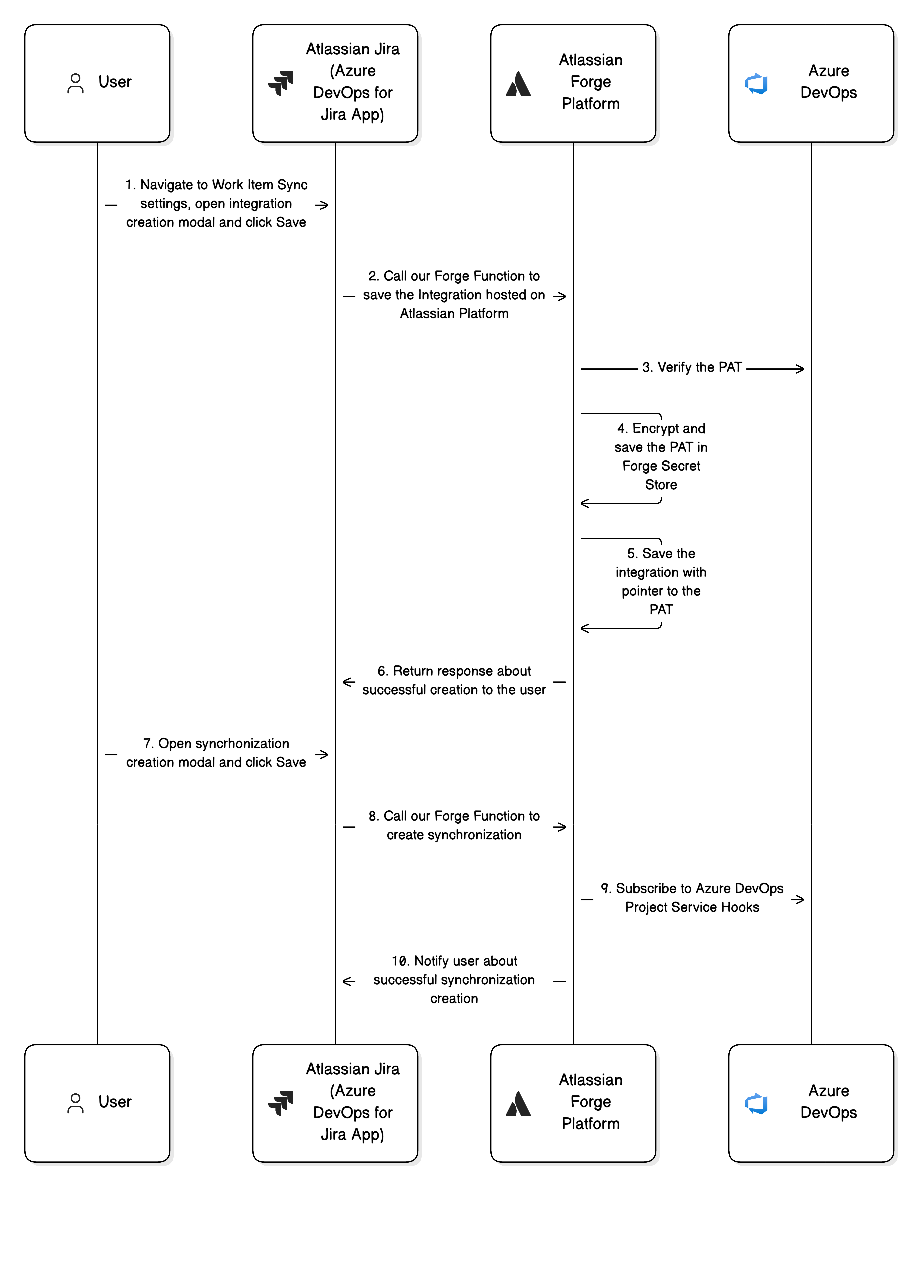
Work Item Sync Setup Flow
Azure DevOps Webhook Processing Flow
External systems
-
dev.azure.com,vsrm.dev.azure.com,app.vssps.visualstudio.com,vsaex.dev.azure.com- or your Azure DevOps Server host -
login.microsoftonline.com- OAuth for Create branch -
Jira Cloud REST API - via the Forge platform
Dev Activities in Jira
Setup
-
Only Jira administrators can create, view or delete integrations.
-
Required PAT scopes: Code (Read), Build (Read), Release (Read). Validated with read-only calls.
-
PAT is stored in the Forge Secret Store; configuration metadata in the Forge Custom Entity Store.
Connecting a project
-
Registers Azure DevOps Service Hooks for code pushes, pull requests (created, updated, merged), build completion, pipeline stage changes and deployments.
-
Each hook is protected by generated credentials stored in the Forge Secret Store.
-
The PAT owner needs the Edit subscriptions permission on the project. If hook creation fails, the connection is rolled back.
Event processing
-
The app authorizes the request, fetches any missing details from Azure DevOps, and sends the development information to Jira.
-
Nothing from the event is stored.
Backfill
-
Imports historical commits, pull requests and branches into Jira - up to two months per run, up to two years back.
-
Stores only run status, selected scope, progress and who started the run.
Creating a branch
-
Uses the user's own credentials, never the integration PAT.
-
OAuth: scopes
vso.code_write,vso.project,vso.profile,offline_access; tokens managed by Atlassian. -
PAT: requires Code (Read & write); stored in the Forge Secret Store.
-
Azure DevOps enforces the user's repository permissions.
Work Items Sync
Setup
-
Only Jira administrators can create integrations.
-
Required PAT scopes by direction:
-
Azure DevOps → Jira: Work Items (Read), Project and Team (Read & write)
-
Jira → Azure DevOps: Work Items (Read & write)
-
Two-way: both of the above
-
-
Member Entitlement Management (Read) is optional - used only to list users when configuring assignee mappings.
Synchronization
-
Registers Service Hooks for work item created, updated and (if enabled) commented.
-
Work item content, comments and attachments are passed between the systems in memory and not stored.
-
The app keeps only identifiers and metadata for deduplication.
-
User mappings (Jira and Azure DevOps user ids and emails) are stored only for users an administrator explicitly maps.
Logs
-
Written to Atlassian Forge logs; retained by Atlassian for 30 days.
-
Contain event metadata only (ids, event types, statuses, errors). Credentials are masked.
-
Site administrators can disable developer access to app logs in Atlassian Administration.
Data retention
-
Configurations remain until deleted by an administrator or the app is uninstalled.
-
On uninstall, Atlassian retains Forge storage for 28 days and then deletes it. Customers can request data recovery from Atlassian within that period.
Note on Azure DevOps Server (on-premises) and static IP
To reach an on-premises Azure DevOps Server when the Static IP option is enabled, the app routes its Azure DevOps traffic through a proxy operated by Move Work Forward on AWS (api.moveworkforward.net, static.moveworkforward.net).
-
The proxy relays requests and responses between Forge and your Azure DevOps host, including inbound Service Hook events. It does not persist the data it relays.
-
Proxy logs are retained for 7 days.
-
All other storage and processing remains on Atlassian Forge as described above.
Updated: September, 2025